Single Sign-On
Connect your identity provider (IdP) to CloudZero to enable single sign-on (SSO). SSO lets your users log in to CloudZero from their IdP without needing a separate CloudZero username and password.
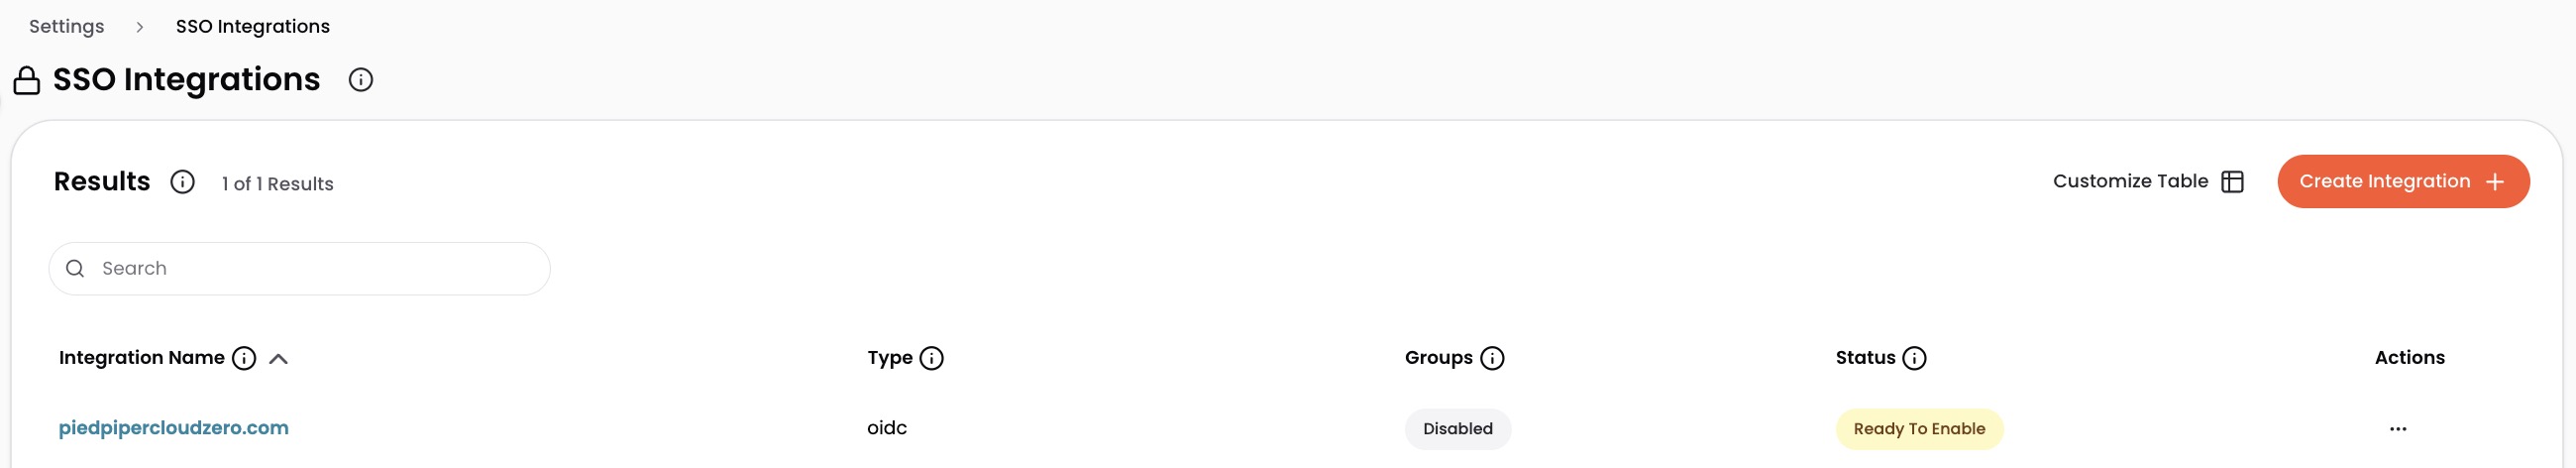
SSO integrations are managed in Settings > SSO Integrations.
Choose your identity provider
CloudZero supports OIDC and SAML 2.0. If your IdP supports both and your organization does not require a specific protocol, OIDC is simpler to configure. If you use Google and want Google groups to control CloudZero Role assignments, use SAML; Google's OIDC tokens don't include group membership.
| Identity provider | Protocol | Guide |
|---|---|---|
| OIDC or SAML | Set Up SSO with OpenID Connect or SAML | |
| Microsoft Entra ID (Azure AD) | OIDC | Set Up SSO with Microsoft Entra ID |
| Okta | OIDC or SAML | Set Up SSO with Okta (OIDC) or SAML |
| OneLogin | OIDC or SAML | Set Up SSO with OpenID Connect or SAML |
| Ping Identity | OIDC or SAML | Set Up SSO with OpenID Connect or SAML |
| Other OIDC provider | OIDC | Set Up SSO with OpenID Connect |
| Other SAML 2.0 provider | SAML | Set Up SSO with SAML |
To have your IdP automatically manage CloudZero Role assignments, see Manage Roles with SSO.
To filter each user's data access by their SSO attributes, see Filter by SSO Login Attribute.
To delete an existing SSO integration, see Delete an SSO Integration.
If any users in your organization have installed the VS Code Extension, they must re-authenticate with CloudZero after changes to your SSO configuration.
Have questions or feedback? Reach out to your account manager.
Updated 12 days ago